This article was created by
Share this article!
Written by Federico Plantera, Researcher and Journalist
When the European Union established the European Peace Facility (EPF) in 2021, it created something that had been missing from its foreign policy toolkit: a mechanism to support the defence and military institutions of partner countries directly, including in cyberspace. Five years on, the cyber component of the EPF has moved from concept to operational reality, with projects running across several countries and a growing body of practical experience about what it takes to build military cyber defence capacity where little or none existed before.
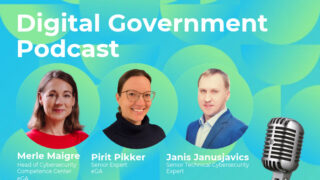
In this episode of the Digital Government Podcast, Merle Maigre, Head of Cybersecurity at the e-Governance Academy (eGA), speaks with Pirit Pikker, senior cybersecurity expert and project team lead for several EPF cyber projects, and Janis Janusjavics, senior technical cybersecurity expert. The conversation draws on their direct experience implementing cyber defence assistance in Ukraine and Moldova – two countries where the stakes could hardly be more concrete.
The building blocks of a credible cyber defence system are broadly the same, whether civilian or military. Janusjavics walks through them in layers: “First and maybe most important of all – people, because you have to have the trained personnel for the running of cybersecurity operations, and you have to have retention of the people because they might leave.” Then foundational hygiene – identity management, segmentation, backups, hardening. “Roughly 80% of the real-world incidents could be stopped if we would keep good foundational hygiene, and this is one of the cheapest layers as well,” Janusjavics says.
Visibility comes next: centralised logging, endpoint telemetry, network sensors, and the analysts trained to read what those systems surface. “You have to have eyes on your infrastructure,” Janusjavics explains. Without tested playbooks and the organisational authority to act during an incident, a security operations centre produces data that nobody responds to. The people question runs through every layer – and budget, Janusjavics adds, has to cover the sustained operations of infrastructure and personnel alike, “not only the people as such, but the training and operations of all the hardware and software.”
In Moldova, roughly four million euros support the upgrading of armed forces’ cyber architecture – routers, switches, servers, multi-factor authentication, vulnerability management – alongside a training programme matched to the new capabilities being introduced. The sequencing of those deliveries turns out to matter enormously. “Licencing for software starts at the point when it is delivered to the customer,” Janusjavics explains. “But if you are not starting to use the product, you’re just wasting your licence.” The alternative is to separate deliveries so that capability builds organically, “like pieces together” – each component layered onto the last, with the organisation absorbing as it goes.
This is what Pirit Pikker calls structural maturity: “Truly understanding the structural maturity of your beneficiary is one of the biggest lessons identified from the Moldova project, because that really drives your implementation.” How well an organisation absorbs assistance, handles schedule changes, adapts when the process runs into friction – that capacity determines what a project can realistically deliver.
Then there is the broader organisational culture and internal procedures that influence how trust operates within the institution itself. “In most cases, if the implementation environment is a bit more complex or the structural maturity is a bit lower, it’s not an issue,” Pikker says. “It’s more about being aware of what they are, because that’s how you can mitigate it, and that’s how you can deliver a better result.”
The global context presses in as well. Supply chain disruptions and shifts in trade, geopolitics, complicate procurement timelines for cybersecurity equipment. During the Ukraine project, Maigre recalls realising mid-implementation that a generator had to be procured alongside the cyber lab hardware, after heavy attacks on Ukrainian energy infrastructure began in late 2022. It had not been part of the original package. Flexibility, adaptive capacity – on both the implementer’s and the beneficiary’s side – is what kept those projects moving.
Before any procurement list is drawn up, the relationship has to be built. Janusjavics is clear about the sequence: “First is to gain the customer’s trust, and the customer’s trust is gained by showing that you are competent in the area you are providing help with. When you gain that trust, then you can actually start the planning work.” In EPF language, this begins with a post-adoption mission – an exploratory visit to understand needs, map stakeholders, assess site facilities, and gauge the existing power relations within the beneficiary’s organisation.
“We truly show that our interest is to help build capabilities. We don’t really have any other motives. There are no wrong answers or wrong points from their end,” Pikker explains. And for countries receiving defence assistance, the assurance that the implementing partner has no agenda beyond capability-building is itself a precondition for honest information-sharing about gaps and weaknesses.
Could you also build capacity and train, as fighting ensues? Realistic, repeated exercises build what Janusjavics calls “muscle memory” in cyber defence teams. “When the real cyber incidents are happening, they are not thinking what should I do – they are reacting to what they actually got the training.”
In a domain where seconds matter and adversaries do not wait, that instinctive competence may be the most durable form of capacity a project can leave behind. It is also why the military dimension of cybersecurity assistance matters at the European level. “Cyber security doesn’t have borders. Having European tools that also work with the defence and military side is important for a broader, comprehensive strength when we talk about cybersecurity in Europe,” Pikker concludes.
This podcast and podcast blog were produced as part of the project “European Peace Facility Assistance on cyber defence in Moldova”, with financial assistance from the European Union via the Technical Support Instrument. The information and views set out herein are those of the author(s) and do not necessarily reflect the official opinion of the European Union or its institutions.